Kudankulam Files Posted On Dark Web, NPCIL Says No Safety Risk
ECONOMY & POLICY

Kudankulam Files Posted On Dark Web, NPCIL Says No Safety Risk

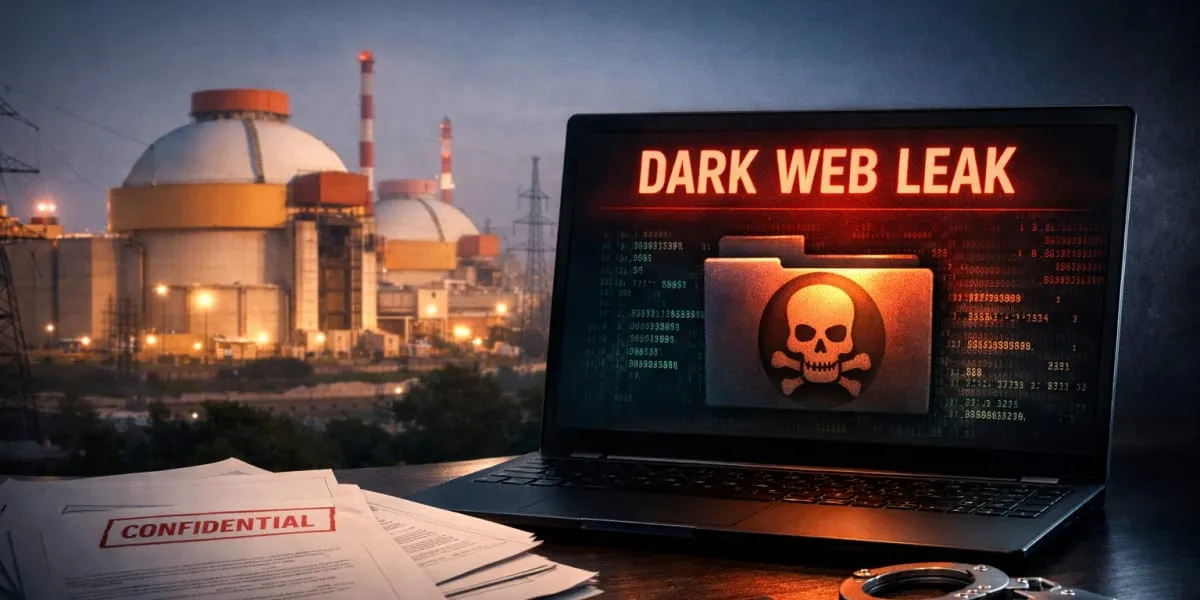
About 19,000 files relating to the Kudankulam Nuclear Power Project in south Tamil Nadu, the largest nuclear facility in the country, were posted on the dark web by a ransomware group called World Leaks, prompting concern in national security and nuclear establishments. Reuters reported that the group asserted the material formed part of more than 0.85 mn documents that it said were obtained by hacking members of the Reliance Anil Ambani group. The disclosure has led to heightened scrutiny by cybersecurity and government agencies.

The Nuclear Power Corporation of India Ltd (NPCIL) stated that no drawings, data or information connected to nuclear safety or nuclear security systems were compromised, and clarified that engineering, procurement and construction work carried out by Reliance Infrastructure pertains only to commissioning of common service facilities. NPCIL emphasised that these facilities are conventional in nature and similar to those used in thermal power plants and other process industries, and that they are not linked to nuclear safety or nuclear security systems. The corporation indicated that it was coordinating with relevant agencies on the matter.

Media reports and agency accounts indicated that the leaked material included blueprints and details of ventilation and cooling systems for Units three and four, which are under construction by a firm of the Anil Ambani Group. Reliance Infrastructure informed agencies that a partial data breach had occurred at a third party service provider engaged by the firm and that the government had been notified. The incident prompted the Computer Emergency Response Team India (CERT-In) to begin an investigation and has drawn attention to supply chain vulnerabilities.

While officials continue to assess the extent of the breach and the identities of those responsible, authorities have underlined that current assessments do not show compromise of nuclear safety or security systems. Investigations are ongoing and agencies are coordinating technical reviews and mitigation measures. The episode has nevertheless reinforced calls for tighter oversight of third party data handling in critical infrastructure projects.

About 19,000 files relating to the Kudankulam Nuclear Power Project in south Tamil Nadu, the largest nuclear facility in the country, were posted on the dark web by a ransomware group called World Leaks, prompting concern in national security and nuclear establishments. Reuters reported that the group asserted the material formed part of more than 0.85 mn documents that it said were obtained by hacking members of the Reliance Anil Ambani group. The disclosure has led to heightened scrutiny by cybersecurity and government agencies. The Nuclear Power Corporation of India Ltd (NPCIL) stated that no drawings, data or information connected to nuclear safety or nuclear security systems were compromised, and clarified that engineering, procurement and construction work carried out by Reliance Infrastructure pertains only to commissioning of common service facilities. NPCIL emphasised that these facilities are conventional in nature and similar to those used in thermal power plants and other process industries, and that they are not linked to nuclear safety or nuclear security systems. The corporation indicated that it was coordinating with relevant agencies on the matter. Media reports and agency accounts indicated that the leaked material included blueprints and details of ventilation and cooling systems for Units three and four, which are under construction by a firm of the Anil Ambani Group. Reliance Infrastructure informed agencies that a partial data breach had occurred at a third party service provider engaged by the firm and that the government had been notified. The incident prompted the Computer Emergency Response Team India (CERT-In) to begin an investigation and has drawn attention to supply chain vulnerabilities. While officials continue to assess the extent of the breach and the identities of those responsible, authorities have underlined that current assessments do not show compromise of nuclear safety or security systems. Investigations are ongoing and agencies are coordinating technical reviews and mitigation measures. The episode has nevertheless reinforced calls for tighter oversight of third party data handling in critical infrastructure projects.

Related Stories

Gold Stories

Next Story
Infrastructure Urban

KONE Opens India's First Digital Experience Centre in Pune

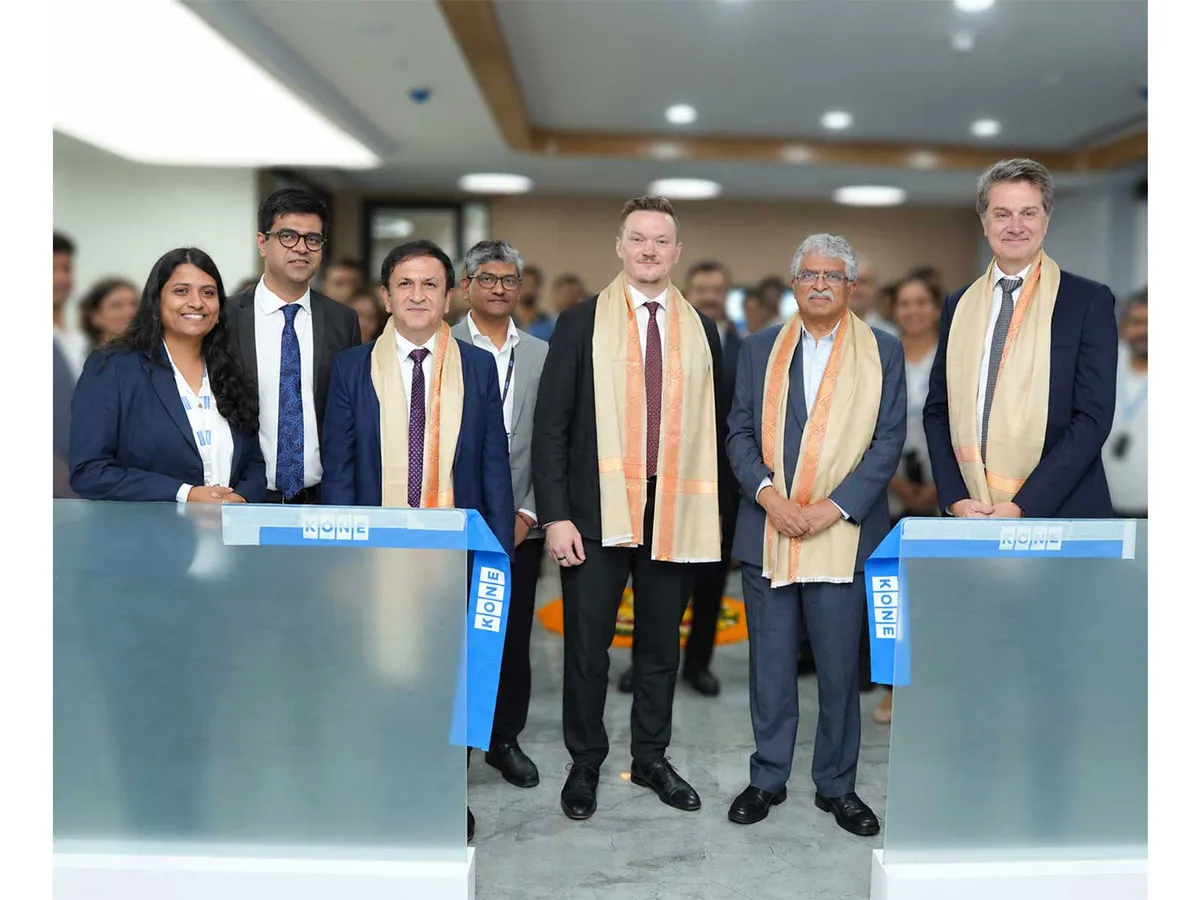
KONE, a global elevator and escalator manufacturer, has inaugurated its first Digital Experience Centre (DEC) in India, located in Pune. The facility aims to showcase how artificial intelligence (AI), connectivity and data-driven technologies can enhance customer experiences and improve building operations.The centre was inaugurated by Jussi Herlin, Executive Vice Chair, KONE Corporation; Philippe Delorme, President and CEO, KONE; and Nandan Nilekani, Co-founder and Chairman of the Board, Infosys.Designed as an interactive customer environment, the facility demonstrates digital solutions cover..
Next Story
Infrastructure Urban

CII GreenCo Launches Circularity Guidelines for Indian Industry

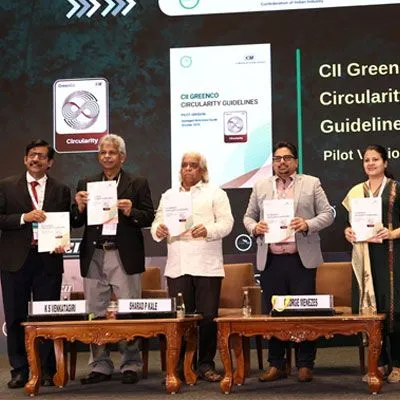
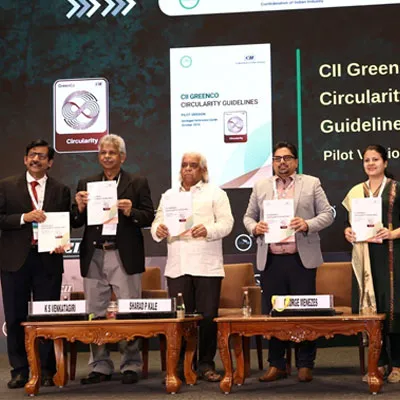
The Confederation of Indian Industry (CII) GreenCo Council has launched the CII GreenCo Circularity Guidelines – Pilot Version at the 17th CII GreenCo Waste & Resource Management Summit 2026 in Chennai. The initiative aims to strengthen resource efficiency, waste reduction and circular economy practices across Indian manufacturing and process industries.The guidelines introduce a structured framework with circularity indices covering raw materials, consumables, packaging and other resource inputs. These indicators will help industries assess existing practices, identify opportunities to ..
Next Story
Infrastructure Energy

Global Electronics Association Launches IPC-1783-CO2E Standard

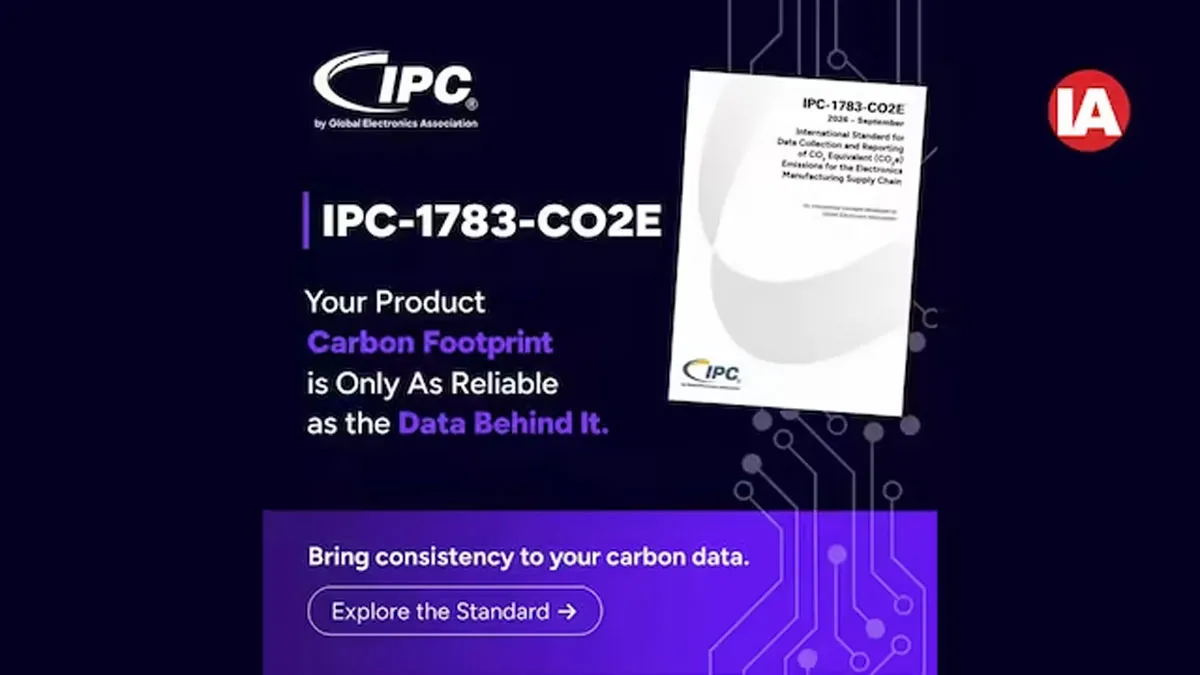
The Global Electronics Association has introduced IPC-1783-CO2E, a new international standard aimed at improving consistency, transparency and comparability in product carbon footprint reporting across the electronics manufacturing industry.The standard, titled International Standard for Data Collection and Reporting of CO2 Equivalent (CO2e) Emissions for the Electronics Manufacturing Supply Chain, provides industry-specific guidance for collecting, estimating and reporting carbon emissions data.With increasing regulatory requirements and customer expectations, electronics manufacturers face c..

Advertisement

Subscribe to Our Newsletter

Get daily newsletters around different themes from Construction world.

STAY CONNECTED

Advertisement

SPECIAL OFFER
QR Code